AuthZed is a centralized authorization platform built by the team behind the open source SpiceDB. It lets companies define permissions once and enforce them across apps, RAG pipelines and AI agents at scale.
AuthZed is an authorization platform that lets engineering teams define who can access what in one place and enforce those rules across every application, service and data source. It is the commercial company behind SpiceDB, an open source permissions database with a public GitHub repository, and it offers a hosted cloud product for teams that prefer not to run the infrastructure themselves.
The platform targets companies that have outgrown permission checks scattered through application code. Typical buyers are platform and security engineers at SaaS vendors, AI product companies, marketplaces and financial firms. The homepage organizes its use cases into three groups: collaboration (sharing and link access, team-based access control), governance (customer-managed permissions, replacing legacy authorization) and querying (retrieval-augmented generation, permission-aware lists and search). The RAG scenario is the most relevant to the AI market, since it keeps LLM applications and agents inside the data boundaries each user already has.
In practice, teams describe their permission model in a flexible configuration language, store relationships between users, groups and resources, and then ask the system whether a given subject may act on a given object. Because rules are defined once and enforced everywhere, changes to business requirements are meant to happen in the schema instead of in rewritten code. The vendor stresses strong consistency guarantees, so a revoked permission is reflected uniformly across systems, along with global scale and low latency. Access to the cloud product starts with a sign-up, and a demo can be booked for larger evaluations.
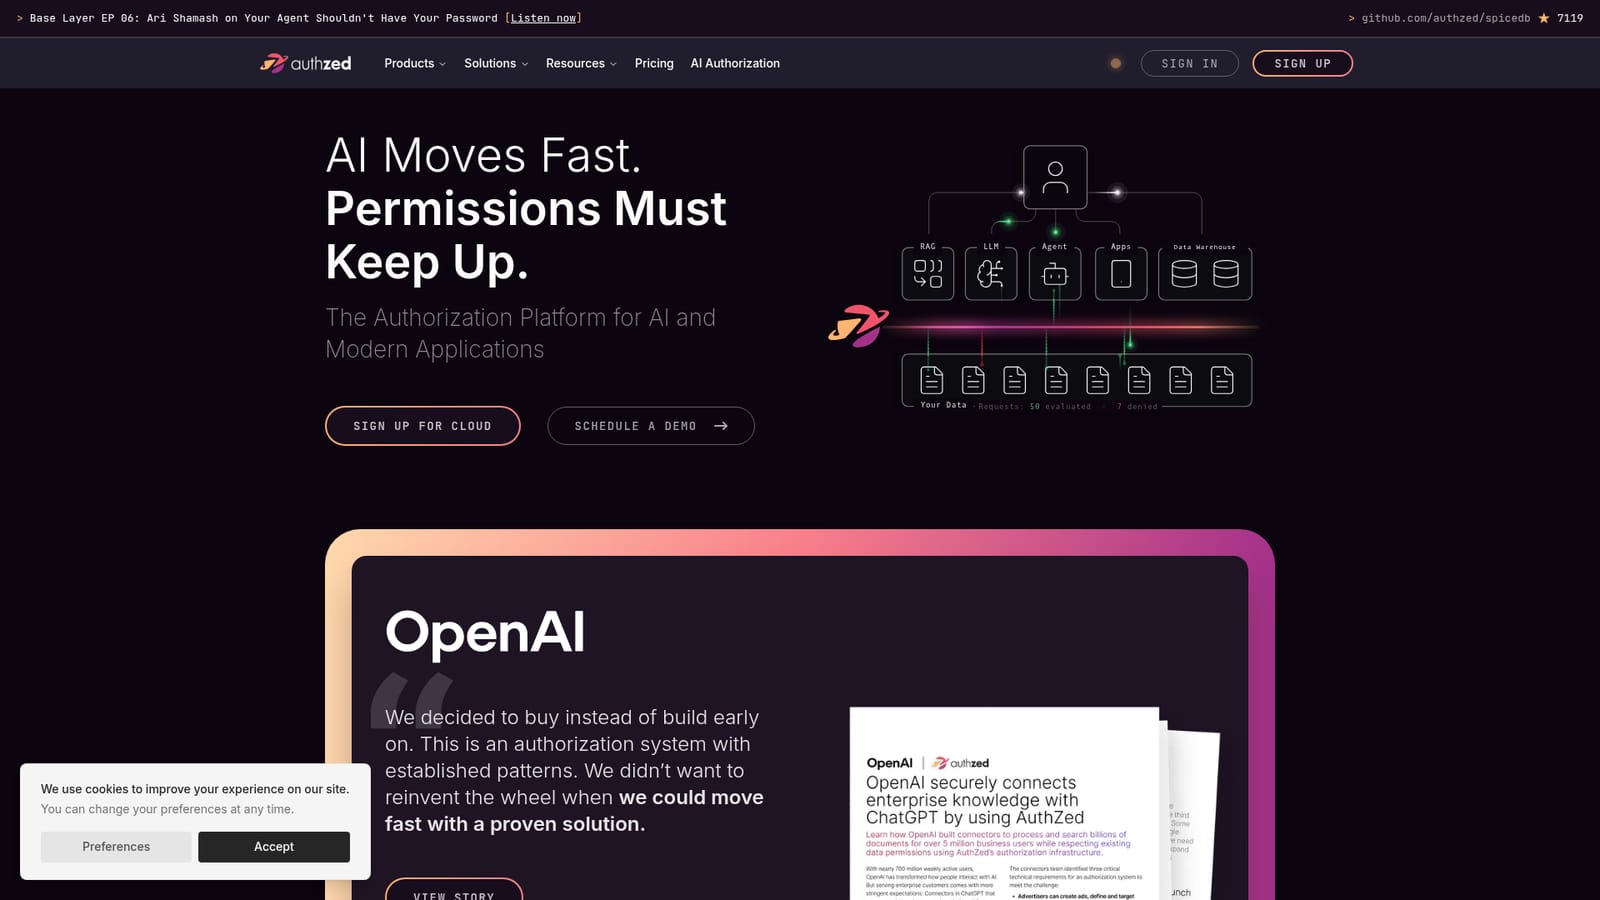
Among alternatives, AuthZed sits in the dedicated authorization service category, as opposed to identity providers that focus on login, or home-grown role checks inside each service. Its customer list includes OpenAI, whose engineer describes buying rather than building an authorization system, plus names such as Workday, Zoom, HackerRank and Redpanda. That makes it a credible option for teams wanting a proven design, though adopting a central permissions service does require modeling work up front.