depthfirst is an AI-native security platform that scans code, dependencies, infrastructure and live environments, validates findings, and proposes fixes through PR reviews, a dependency firewall and agentic pentesting.
depthfirst is a security platform built around AI agents that behave like a research team inside an organization's software stack. It covers source code, third-party dependencies, infrastructure and the running environment, with the aim of detecting vulnerabilities, validating which ones are real, and helping teams remediate them. The vendor positions it as continuous cyber defense rather than a point scanner.
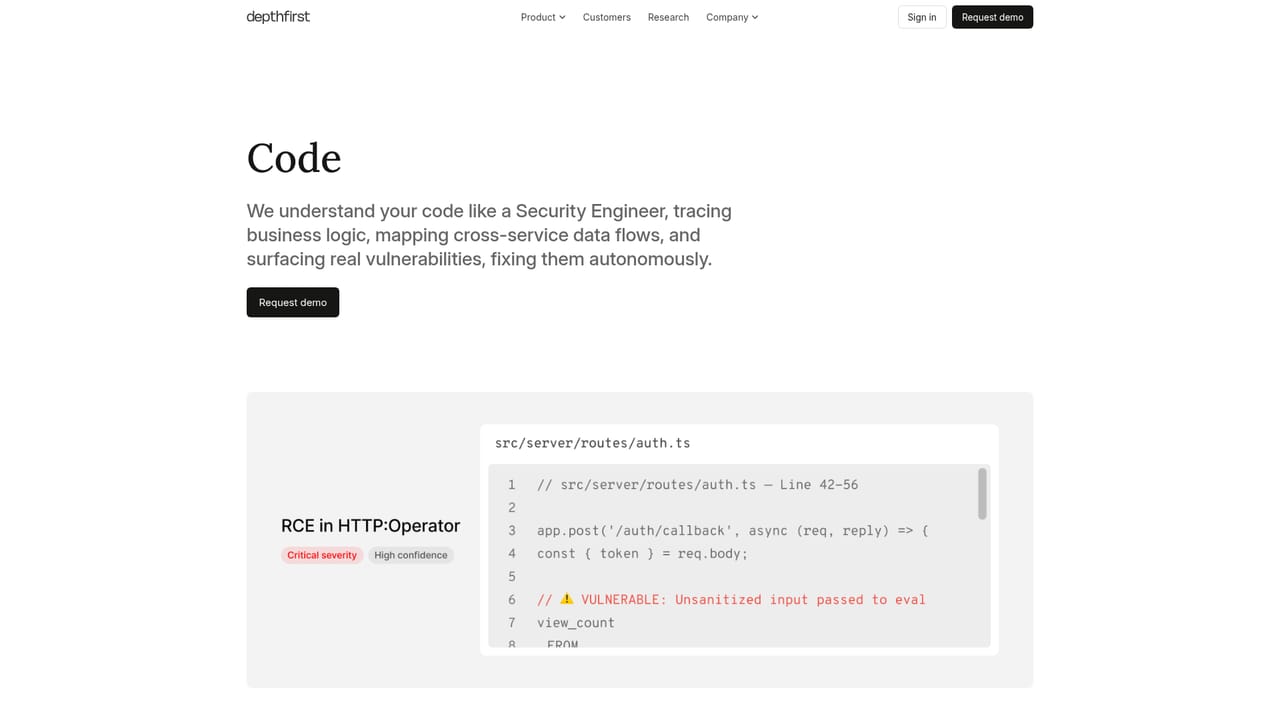
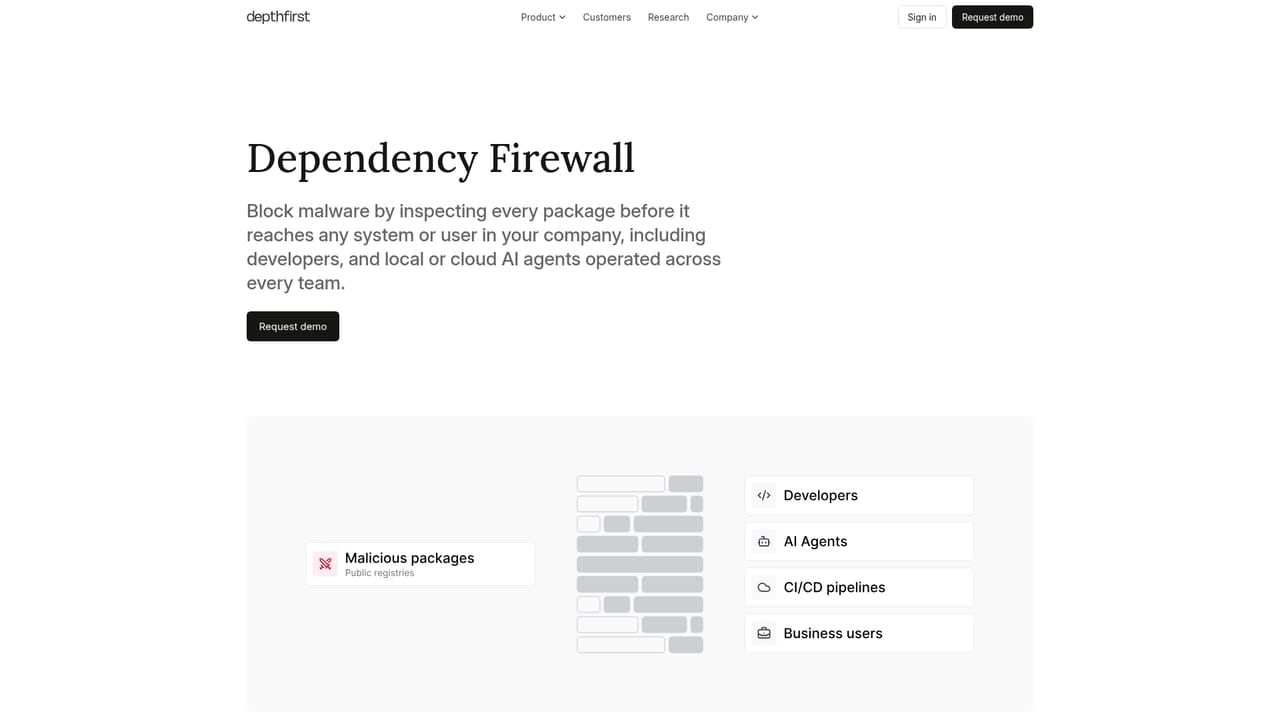
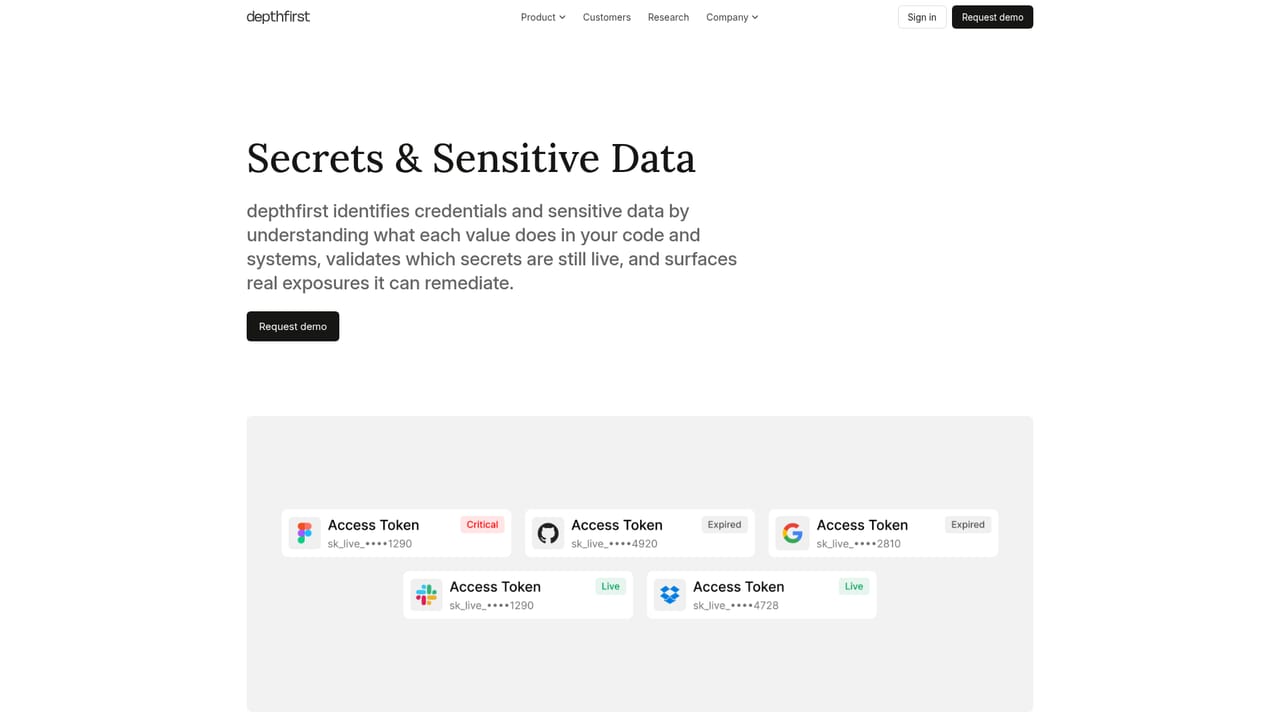
The product line is split into several modules visible on the site: code review, a Dependency Firewall, supply chain protection, secrets detection and Agentic Pentesting, a newer offering that tests applications the way an attacker would. Pull request reviews are a notable workflow. According to customer quotes, the reviewer proposes concrete code changes that developers can apply directly in the pull request, and it tracks context across scans so its findings improve over time. Customers such as Supabase, Persona, AngelList and Moveworks describe using one or more of these modules.
Under the hood, depthfirst trains its own security-specific models and agents, including a model called dfs-large1, and publishes a benchmark named dfbench that measures detection recall, validation precision and differential analysis across many frontier models. The site charts these results against cost per task, which signals that cost efficiency is a stated design goal. A research section also covers vulnerability work such as GitLab remote code execution findings and container security.
The audience is security and engineering leaders at software companies that want to reduce manual security-engineering effort without adding headcount. Adoption starts with a demo request rather than self-serve signup, so it suits organizations with a formal security function. Among alternatives, it competes with traditional static analysis and dependency scanners by emphasizing validation and fix proposals over raw alert volume, though buyers will need to evaluate the vendor's claims against their own codebases.