Integrations
Listed integrations include Claude Code, Claude Desktop, Codex, Cursor, GitHub, GitLab and Slack, with more available. The platform layer cites MCP, Insights, API and SCM, and notifications flow through GitHub, GitLab and Slack.
AI-native SAST that validates real risk before code ships
Own DryRun Security? Verify ownership to get a dofollow link

DryRun Security is an AI-native code security platform that models your application, then reviews pull requests and full repositories for exploitable risk. It replaces regex rule libraries with contextual agents, adds natural language policies, and posts findings where developers already work.
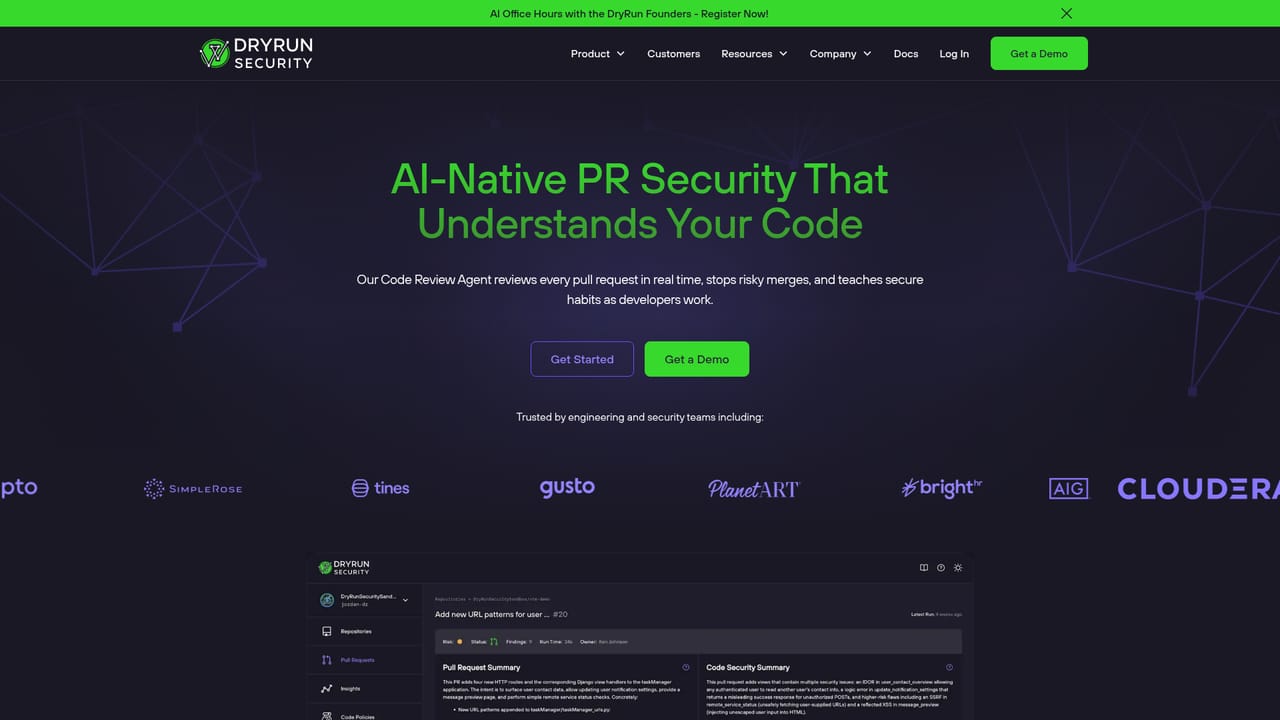
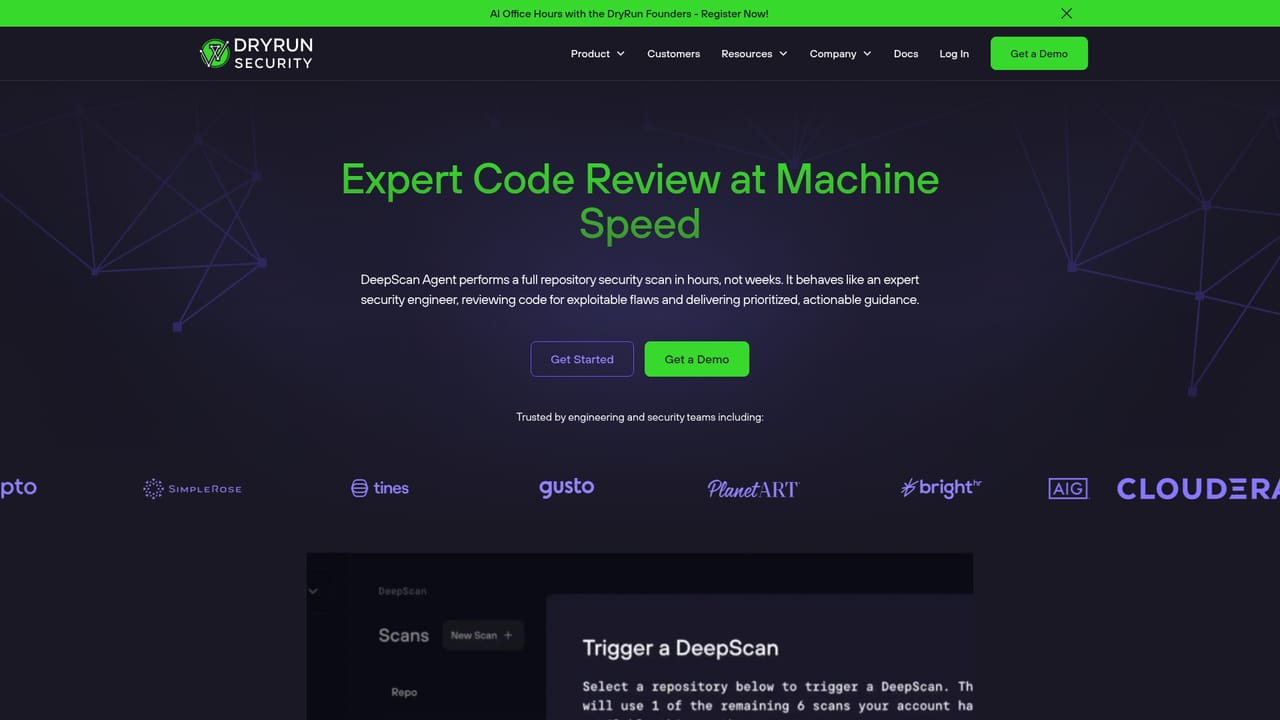
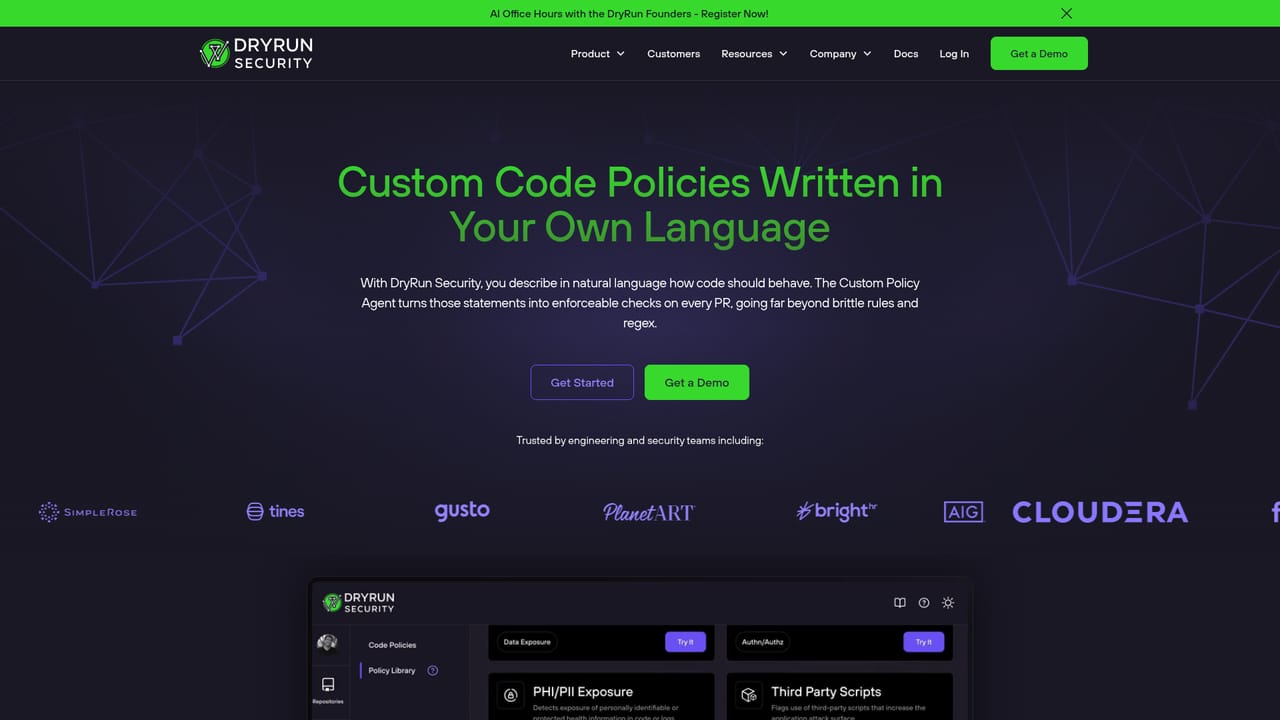
DryRun Security is an application security platform built around AI agents that review code the way a senior security engineer would. Rather than matching patterns from a rule library, it builds a working model of the application first: architecture, service relationships, frameworks, routes, authorization boundaries and data flow. Every pull request and repository scan is then judged against that model, so findings reflect how the code actually behaves inside the system rather than how a snippet looks in isolation. The product spans several connected surfaces. AI-native SAST covers injection, authorization, IDOR and logic flaws, while PR Code Review posts context, security findings and change summaries directly into pull requests. A DeepScan agent runs a full repository baseline to surface structural risk that predates any single change, and Custom Code Policies let a team express its own rules in natural language so they are enforced on each subsequent change. Triage and trend tracking sit on top, with an underlying knowledge graph of findings, summaries and application behavior that updates as the codebase evolves. It is aimed at engineering and security teams that already ship fast and now also review code written by AI assistants. The homepage pitches DryRun as an independent verification layer for both human and machine-written code, and lists Claude Code, Codex, Cursor, GitHub, GitLab, Slack and MCP among the surrounding tooling, plus MCP, Insights and API on the platform side. Coverage is stated for Python, JavaScript, TypeScript, Java, C#, Ruby and Golang, with more available on request. The contrast with classic SAST is the central claim: no regex or rule groups to author and maintain, roughly double the accuracy in PR and repository reviews, and about ninety percent less noise thanks to exploitability scoring. Setup is described as a matter of minutes for connected code hosts. Teams weighing established scanners will find the pitch strongest where rule maintenance has become a burden and where AI-generated code has outrun traditional review capacity.
Listed integrations include Claude Code, Claude Desktop, Codex, Cursor, GitHub, GitLab and Slack, with more available. The platform layer cites MCP, Insights, API and SCM, and notifications flow through GitHub, GitLab and Slack.
AI-native SAST using a Contextual Security Analysis engine, PR code reviews with findings and change summaries, a DeepScan agent for full repository baselines, natural language custom code policies, and triage with risk trend tracking. An underlying knowledge graph of findings, code summaries and application behavior updates continuously, and the platform exposes MCP, Insights and API surfaces.
Learn more AI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplay
 Candy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.
 ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voiceAI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplayCandy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voice


