Support
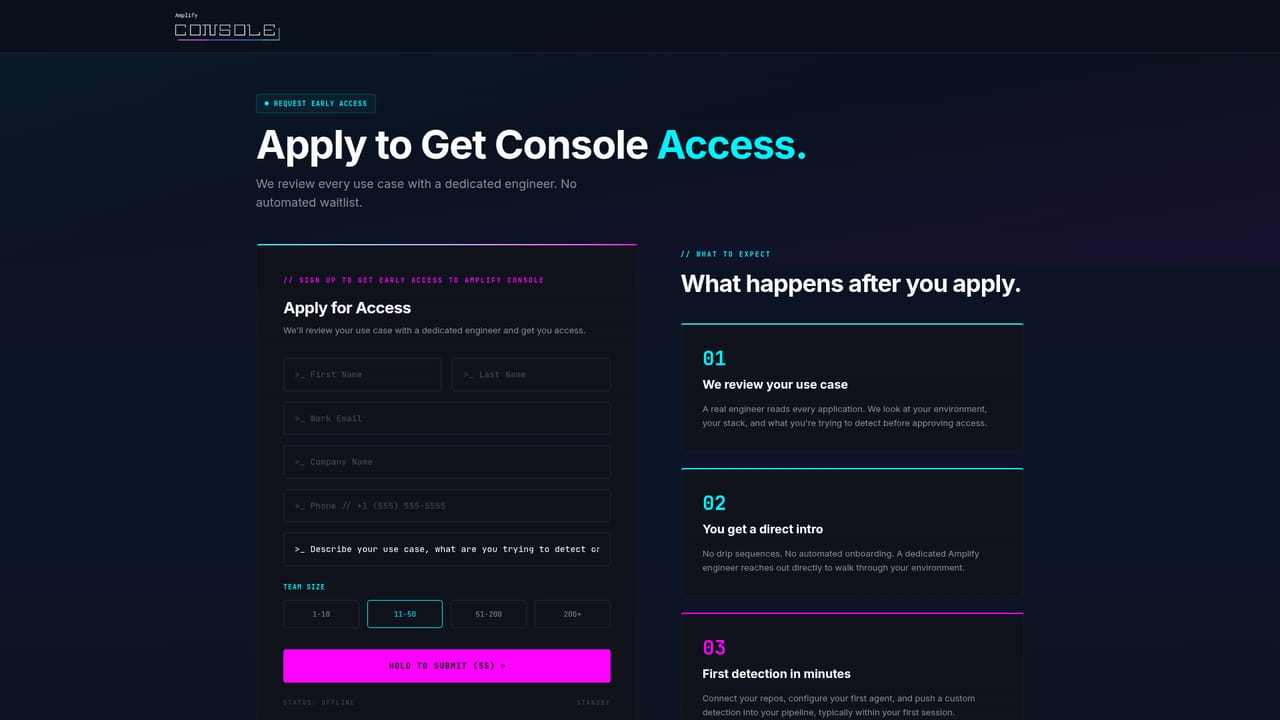
Support runs through documentation and direct contact. Access requests are reviewed with a dedicated engineer, and the site offers a contact channel and request access form.
Learn moreCustom detection agents for security engineers, run on managed cloud plumbing
Own Amplify Security? Verify ownership to get a dofollow link

Amplify Security is a cybersecurity tool. Amplify Security's Console lets security engineers write, test and deploy custom detection agents into their own cloud pipelines, with built in triage, reachability filtering, automated remediation and reporting from a single cockpit. Access is reviewed case by case.
Amplify Security is a platform for security engineering teams who want to author their own detection agents rather than accept a fixed vendor rule set. The company positions its product, Amplify Console, as a security harness: engineers describe the detections they care about, and the harness compiles those agents, deploys them into the customer's cloud environment (the site shows a production VPC example), and tracks them over time. The pitch is aimed squarely at teams already using coding assistants and finding that general purpose models do not understand the security workflow of discovering, creating, deploying, tracking and reporting on custom detections. The console is organized around a handful of subsystems. Custom agents are created, tested, iterated and deployed from the interface. Custom triage pulls alerts from any source and applies rules based on company priorities. A reachability engine filters out vulnerabilities that cannot actually be reached or exploited, which is the part most directly contrasted with legacy scanners. An auto fix engine offers one click remediations that can be customized and shared with developers. Integrations tie the whole thing to existing security tooling and pipelines. It fits best in organizations with dedicated detection or product security engineers, roughly the Series C and enterprise profile implied by the customer quote on the homepage. Smaller teams without someone who can write and maintain rules will get less out of it, since the authoring burden sits with the customer. Compared with Snyk, Semgrep and the Checkmarx and Veracode class of tools, Amplify argues that competitors stop at finding issues while it orchestrates fixes and keeps findings live and collaborative rather than static. Access is gated. Prospective users apply for early access, and the company says it reviews each use case with a dedicated engineer before granting entry. That review process is worth factoring into procurement timelines.
Support runs through documentation and direct contact. Access requests are reviewed with a dedicated engineer, and the site offers a contact channel and request access form.
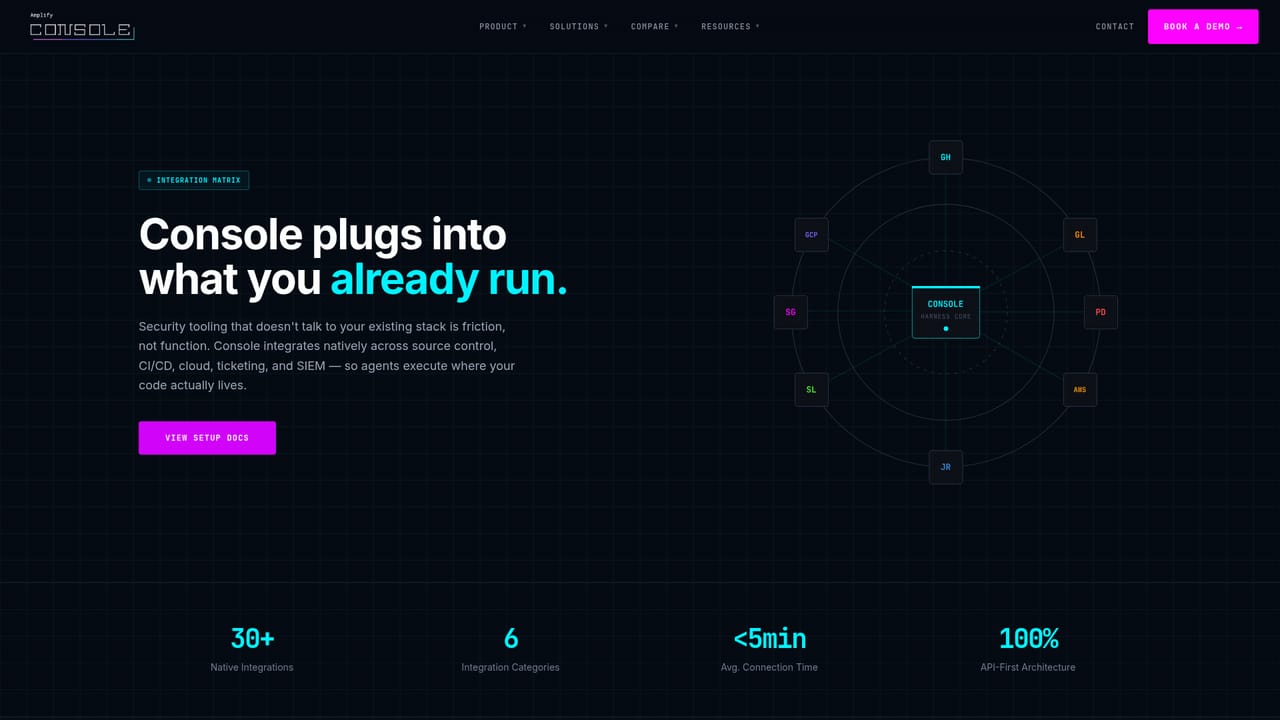
Learn moreConsole is described as integrating with the security tools already in place, plus source control, CI/CD, cloud and ticketing, set up once. Specific connectors are listed on the integrations page.
Learn moreCustom agent authoring with testing, iteration and deployment; custom triage that ingests alerts from any source and applies company priorities; a reachability engine that removes non exploitable findings; an auto fix engine with one click remediations that can be customized and shared with developers; live, collaborative findings; and narrative based reporting rather than severity only output.
Learn more AI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplay
 Candy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.
 ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voiceAI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplayCandy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voice


