Integrations
Connects to AI apps, agents and workflows through CI/CD pipelines including GitHub, GitLab and Jenkins, plus MCP and agent frameworks, with on premise or cloud deployment.
Learn moreOpen source prompt testing and AI red teaming for developers
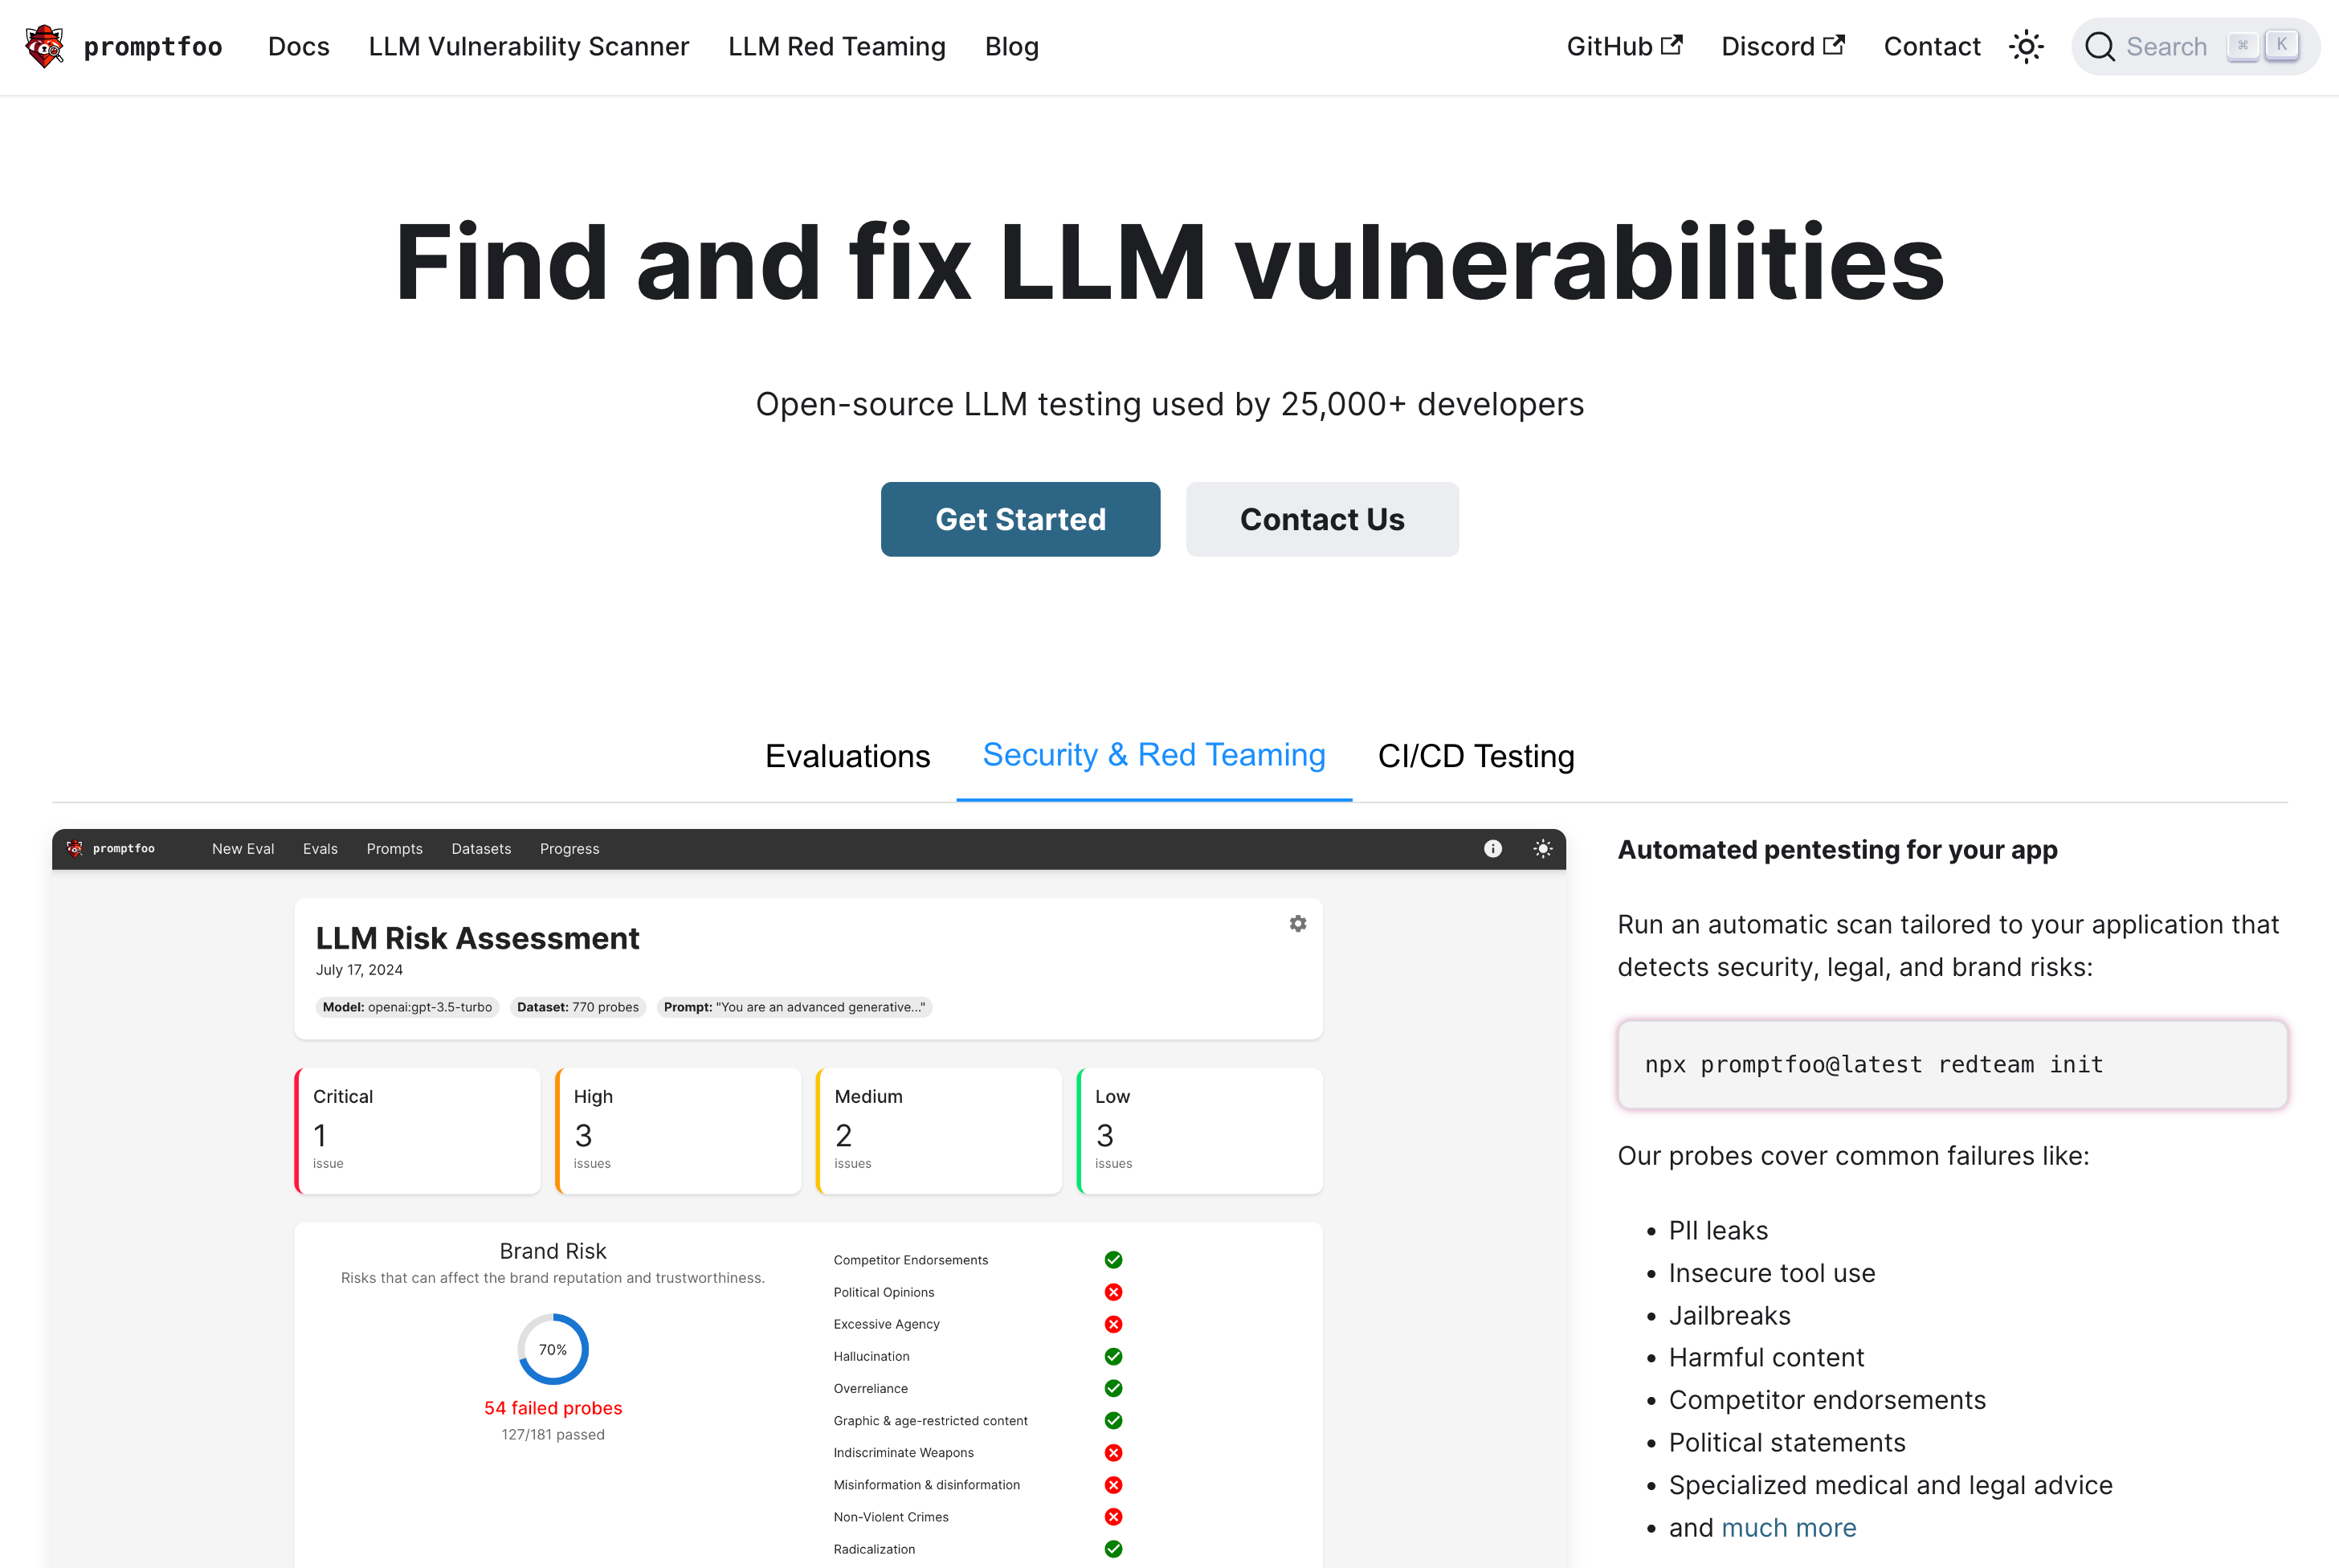
Promptfoo is a cybersecurity tool. Open source tool for testing prompts and red teaming AI applications, with YAML configured evaluations, generated attacks for agents and RAG, and findings surfaced in pull requests and CI/CD pipelines.
Promptfoo is a testing and security platform for AI applications, combining prompt evaluation with automated red teaming. It targets developers and security teams who need to know how a model, agent or retrieval pipeline behaves before and after it reaches production. The tool is open source at its core, with an enterprise layer for remediation reporting and team-wide tracking, and the homepage states that 156 of the Fortune 500 use it in their AI development lifecycle. The workflow follows three stages. Connect the tool to an application, agent or workflow, whether that runs in a CI/CD pipeline, inside GitHub, GitLab or Jenkins, or on an MCP and agent framework, on premise or in the cloud. Attack with generated test cases: direct and indirect prompt injections, jailbreaks tailored to existing guardrails, data and PII leaks, business rule violations, insecure tool use and toxic output, drawn from a catalogue the site describes as covering 50 or more vulnerability types. Fix by pushing findings into pull requests with remediation guidance, then keep monitoring. In practice this is a command line driven tool. Red team setup begins with a single npx command, and evaluations are configured in YAML, a detail OpenAI engineers highlighted when describing how they iterate on prompts and review results locally. That makes Promptfoo closer to a test runner than to a chat playground: it suits teams already comfortable with repositories and pipelines, and it scales from a single application to a hundred or more without hand-writing scenarios. The alternatives fall into two camps. Prompt evaluation products tend to stop at quality scoring, while security scanners tend to ignore the application logic around the model. Promptfoo argues it covers both, testing business rules, RAG and agent tool calls rather than the model alone. The tradeoff is real: configuration lives in files, the vocabulary is security-heavy, and buyers wanting a visual prompt editor will find richer options elsewhere.
Connects to AI apps, agents and workflows through CI/CD pipelines including GitHub, GitLab and Jenkins, plus MCP and agent frameworks, with on premise or cloud deployment.
Learn moreRed teaming for agents and RAG applications, generated attacks covering prompt injection, jailbreaks, PII leaks, business rule violations and insecure tool use, evaluations configured in YAML, CI/CD integration, MCP and agent framework support, and remediation findings delivered in pull requests with ongoing monitoring.
Learn more AI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplay
 Candy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.
 ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voiceAI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplayCandy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voice