Prompt Security by SentinelOne

AI security research, glossaries and open-source agent tooling from SentinelOne

Advanced
Screenshot of Prompt Security by SentinelOne, AI security research, glossaries and open-source agent tooling from SentinelOne

What is Prompt Security by SentinelOne?

Prompt Security by SentinelOne is an AI aggregators tool. SentinelOne's AI security hub: weekly research on agentic AI threats, ChatGPT enterprise risk and AI policy, plus open-source tools for prompt fuzzing, agent skill integrity and OpenClaw deployment oversight.

Prompt Security is SentinelOne's AI security resource hub, aimed at practitioners who have to defend AI systems rather than at buyers shopping for a chat assistant. The site gathers research posts, plain-language glossaries and a small set of open-source utilities in one place, with new material added on a weekly cadence according to the homepage. The editorial side covers the parts of AI risk that tend to get skipped in vendor marketing. Published pieces examine the agentic attack surface where risk sits beyond the prompt itself, the way AI agents can become a hidden control plane inside a supply chain, and a ChatGPT security guide written for enterprise risk and incident response. Three starter glossaries define agentic AI, AI acceptable use policy and AI gateway, giving security and compliance teams a shared vocabulary before they write controls or brief leadership. The practical side is three tools. ClawSec is a security skill suite for AI agents offering drift detection, live recommendations, automated audits and skill integrity verification. OneClaw gives visibility into OpenClaw deployments so teams can track agent activity and usage patterns across an organization. ps-fuzz stress-tests system prompts against dynamic LLM-based attacks, with support for 16 providers and 16 attack types. ClawSec and ps-fuzz are published on GitHub, while OneClaw runs as a hosted tool. The fit is narrow and deliberate. Security engineers, AI platform owners and GRC staff get reference material and testing utilities without a sales call, and the GitHub projects can be inspected before adoption. Anyone looking for a commercial firewall, a runtime guardrail product or a managed detection service will not find pricing, deployment details or SLAs here; this is the research and tooling front door for SentinelOne's AI security work, not a full product console. Prompt Security suits organizations already running LLM features or agents that need to understand the threat model first. Teams starting from zero can read a glossary, run ps-fuzz against a system prompt, and use the blog to build an internal position before evaluating paid platforms.

How do you use Prompt Security by SentinelOne?

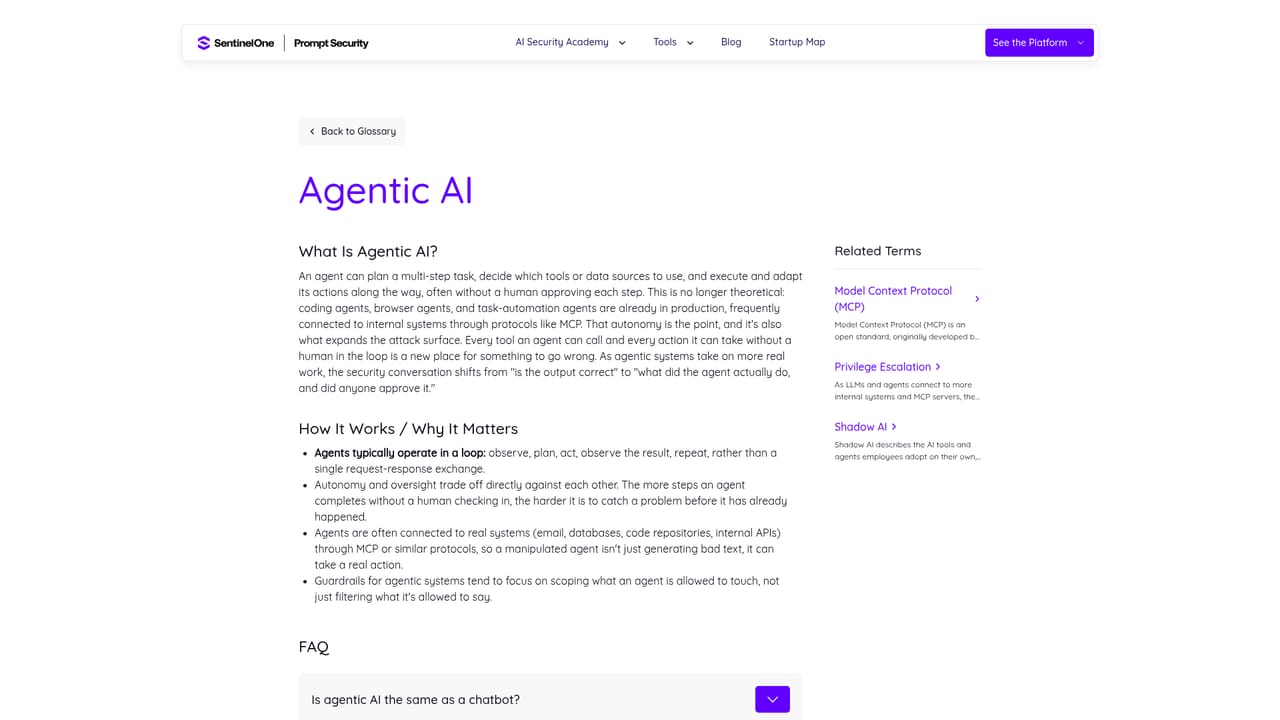
  1. 1Read the agentic AI glossary entry
    Start with the glossary definition of agentic AI to understand how autonomous planning and tool use change the risk model before evaluating any control.
    Prompt Security by SentinelOne — Read the agentic AI glossary entry
  2. 2Map the attack surface with the research post
    Work through the post on where risk lives beyond the prompt to identify which parts of your own agent deployments need testing or oversight.
    Prompt Security by SentinelOne — Map the attack surface with the research post
  3. 3Run ps-fuzz against a system prompt
    Clone the ps-fuzz repository from GitHub and point it at a test system prompt to see how it holds up against LLM-based attacks across providers and attack types.
  4. 4Audit agent skills with ClawSec
    Install the ClawSec skill suite to check agent skills for drift, run automated audits and verify skill integrity before promoting changes.
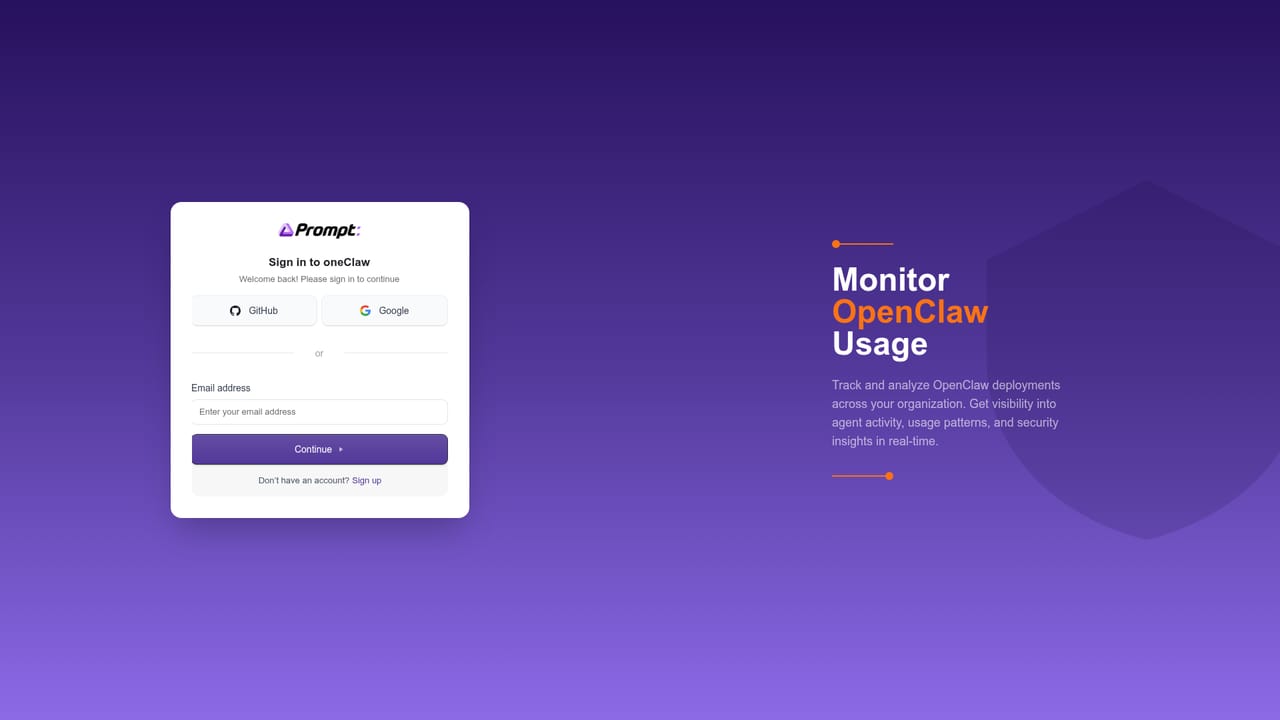
  5. 5Review OpenClaw activity in OneClaw
    Open the OneClaw tool to see agent activity and usage patterns across the organization and flag deployments that need a closer look.
    Prompt Security by SentinelOne — Review OpenClaw activity in OneClaw
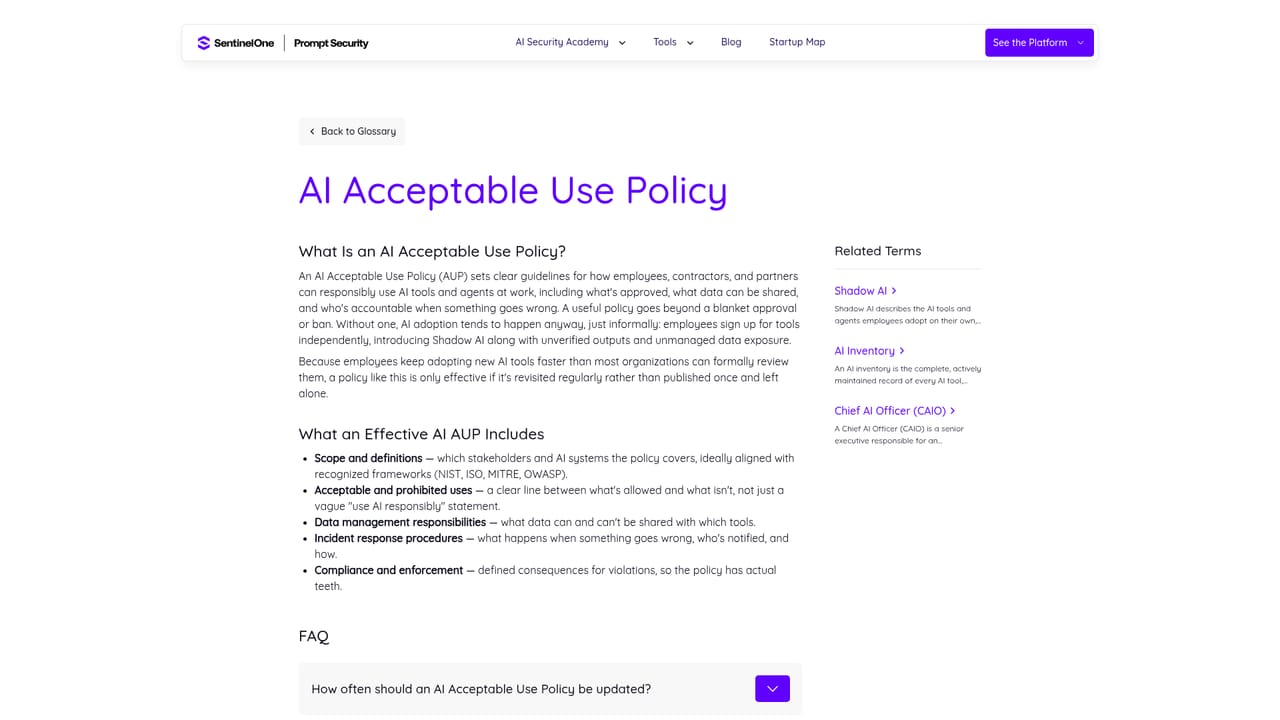
  6. 6Draft an AI acceptable use policy
    Use the AUP glossary entry and the AI policy material to align internal rules on approved tools, permitted data and accountability before rollout.
    Prompt Security by SentinelOne — Draft an AI acceptable use policy

Pros and cons

Pros

  • Free access to original research on agentic AI attack surfaces and enterprise ChatGPT riskAI
  • Open-source tooling on GitHub that can be reviewed and self-hosted before adoptionAI
  • ps-fuzz covers 16 providers and 16 attack types, a practical starting point for prompt hardeningAI
  • Glossaries give security and compliance teams a consistent vocabulary for policy workAI
  • OneClaw adds visibility into OpenClaw agent activity and usage patternsAI

Cons

  • No published pricing, packaging or commercial terms anywhere on the homepageAI
  • The site is a resource hub, not a product console, so runtime enforcement details are unclearAI
  • ClawSec and ps-fuzz require GitHub and command line comfort, not a point-and-click experienceAI
  • Research is skewed toward SentinelOne's own framing of the threat landscapeAI
  • No stated support channel, SLA or documentation portal for the toolsAI

How much does Prompt Security by SentinelOne cost?

Features

Research blog covering agentic AI risk, ChatGPT enterprise security and supply chain concerns for AI agents. Glossaries explain agentic AI, AI acceptable use policy and AI gateways. Open-source tools include ClawSec for agent skill integrity and audits, ps-fuzz for system prompt stress testing across 16 providers and 16 attack types, and OneClaw for OpenClaw deployment visibility and usage analysis.

Learn more

Frequently asked questions about Prompt Security by SentinelOne

  • How do you use Prompt Security by SentinelOne?
    The walkthrough on this page covers 6 steps: 1. Read the agentic AI glossary entry 2. Map the attack surface with the research post 3. Run ps-fuzz against a system prompt 4. Audit agent skills with ClawSec 5. Review OpenClaw activity in OneClaw 6. Draft an AI acceptable use policy.
  • What platforms does Prompt Security by SentinelOne support?
    Prompt Security by SentinelOne is available on Web App.
  • What are the limitations of Prompt Security by SentinelOne?
    No published pricing, packaging or commercial terms anywhere on the homepage. The site is a resource hub, not a product console, so runtime enforcement details are unclear. ClawSec and ps-fuzz require GitHub and command line comfort, not a point-and-click experience.

Status

StatusActive
Views0
Outbound clicks0
Added10/21/2026

Platforms

Web App

Pricing

Free