Free trial
The homepage does not describe a free trial. It offers an instant AI demo that runs a pentest in the browser and a demo booking, neither of which is presented as a trial of the paid platform.
Learn moreAutonomous pentest agents that map what an attacker can actually reach.

Penti is a coding tool. Penti runs autonomous pentest agents across everything a company owns and reports which assets an attacker can actually reach. Certified human testers can validate any finding on any plan, and the vendor publishes an open benchmark of AI models as pentesters on OWASP Juice Shop.
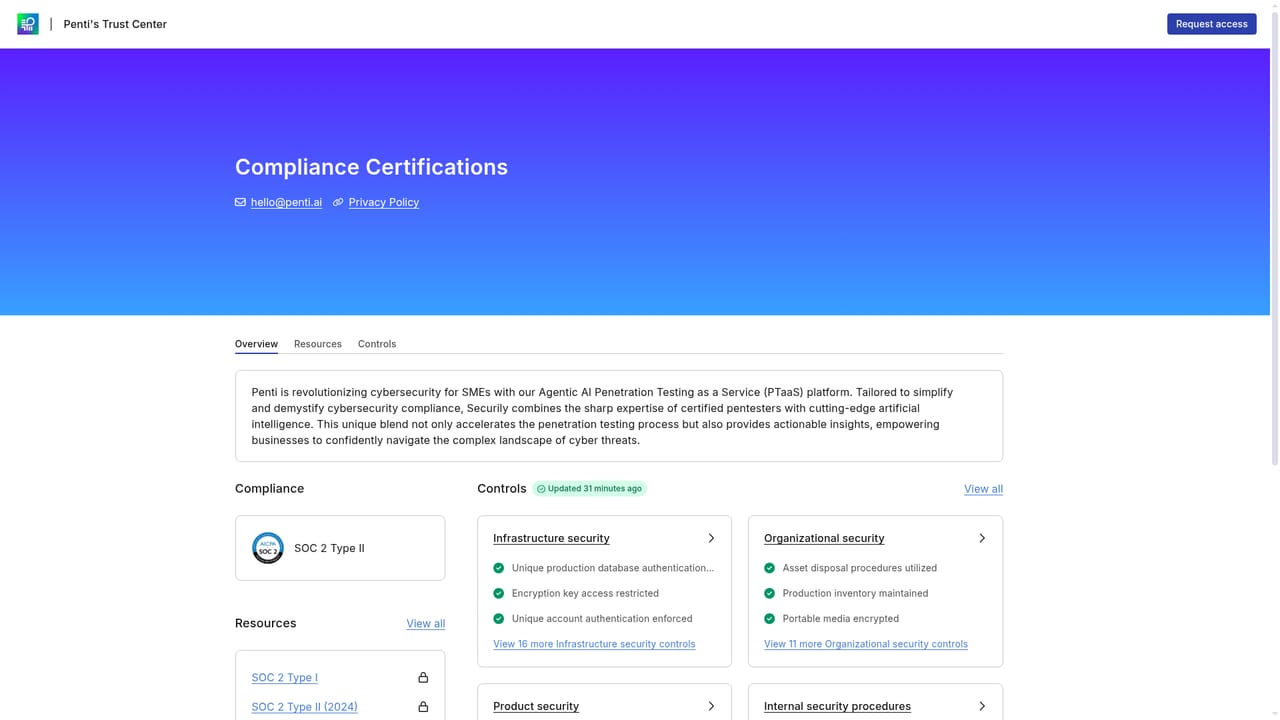
Penti is a penetration testing platform built around autonomous agents rather than a calendar slot with a human consultant. The premise is blunt: most of an organization's attack surface is assumed secure because nobody has tested it. Penti sends coordinated agents across everything the customer owns (web applications, hosts, APIs and the rest of the estate) to attempt the same paths a real intruder would, then reports which findings are genuinely reachable. The homepage frames this as a coverage ledger, where every asset falls into a column: tested and safe, tested and vulnerable, or still unknown. The product runs in phases that will look familiar to anyone who has scoped a traditional engagement. Preflight, discovery and exploitation follow one another, with individual agents reporting live progress such as reverse DNS lookups, schema dumps after a confirmed SQL injection, or an exploit count climbing toward completion. Multiple agents can work in parallel on separate targets, and a run can stretch over hours. What separates Penti from fully automated scanners is the validation layer: on any plan, a certified human pentester can review and confirm a finding before the customer acts on it, which matters when a report will be handed to engineering or used to justify spend. That combination targets security and engineering teams at companies that ship faster than they can schedule assessments. Startups without a dedicated security function can use it to cover surface that annual testing never reaches; larger teams can use it between formal engagements as continuous verification. Penti also publishes PentiBench, an open benchmark of how leading AI models perform as pentesters across 98 official OWASP Juice Shop challenges, which supports its claim of measuring rather than asserting agent capability. The vendor holds SOC 2 Type II and staffs US based testers with offensive certifications including OSCP, CPTS and CEH. Competitively, Penti sits between scanner-first products that surface possible issues and boutique firms that charge for depth on a narrow scope. It sells breadth and speed with a human check at the end, not hand delivered exploit development on demand.
The homepage does not describe a free trial. It offers an instant AI demo that runs a pentest in the browser and a demo booking, neither of which is presented as a trial of the paid platform.
Learn moreSupport runs through a demo booking for sales and scoping questions and a trust portal holding the SOC 2 Type II audit report for security review. No public help centre or ticketing route is listed on the homepage.
Learn moreAutonomous pentest agents run preflight, discovery and exploitation phases in parallel across owned assets, with live progress per agent. Results are sorted into a coverage ledger that separates tested and safe, tested and vulnerable, and untested surface. Certified human testers can validate any finding on any plan. The vendor publishes PentiBench, an open benchmark of AI models as pentesters on OWASP Juice Shop.
Learn more AI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplay
 Candy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.
 ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voiceAI Angels400+ customizable AI girlfriends for NSFW chat, voice calls, and roleplayCandy AIExperience the future of companionship with AI friends who chat, role-play, and connect with you on a human level.ourdream.aiA vast AI roleplay platform with millions of characters for chat, images, video and voice


